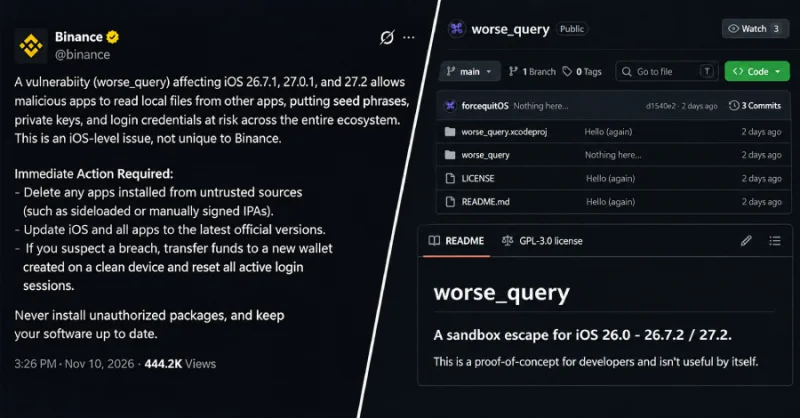
Binance warned that an iOS sandbox escape published on GitHub could let an app read other apps' files on iPhones running iOS 26 and 27, putting seed phrases, private keys and login credentials at risk. The company said people who suspect they may be affected should move funds to a new wallet on a clean device and reset all active login sessions.
The warning landed after Apple's updates for iOS 26 and iOS 27 were released yesterday without any listed fix for the issue. The same updates fixed two iMessage flaws and several Bluetooth bugs, but the security notes did not mention worse_query or any other sandbox problem, leaving users with no clear sign that Apple has addressed the exposure.
The exploit was released on Sunday by forcequit, working with 0xjohnny, and the researcher said the code is meant for developers and is not useful by itself. Even so, other developers have already built installable apps on top of it, which turns a proof of concept into something easier to put in front of users. WQ Files, a file manager built by Christoph Kolbicz, can reach other apps' data without a jailbreak or a kernel exploit, and it can edit, delete and clear that data.
That is the part that makes the warning harder to dismiss. To use the code, an app has to set up an App Group container, and WQ Files installs through sideloading tools such as AltStore and SideStore, which automatically create the App Group WQ Files needs when used with an Apple ID. Binance told users to delete apps installed from untrusted sources, including sideloaded or manually signed apps, and to update iOS and all their apps, but it did not name any wallet app as exposed.
The gap is just as important as the alert: no one involved has said whether an App Store app could use worse_query, and neither Binance nor the researcher has reported any attacks or thefts. In a reply on X, forcequit said he had not planned to release worse_query early, adding that Apple was stalling on responding to him and people started larping with it on here. For now, the issue sits between a published exploit and an unpatched warning, with users told to act before anyone can say exactly which apps, if any, were already at risk.