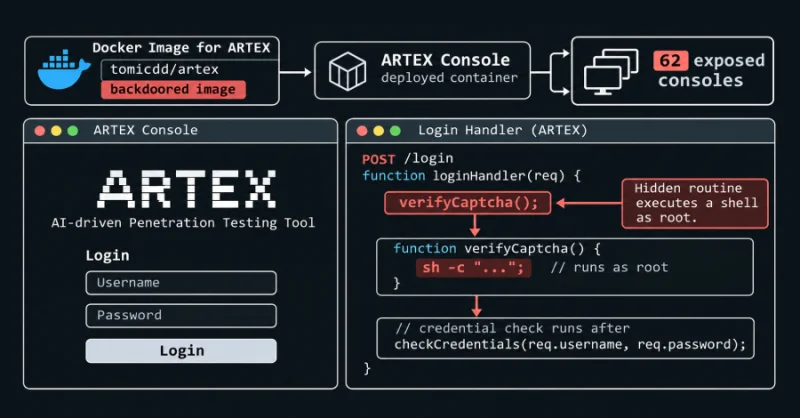
CERT-In has disclosed that an artificial intelligence-assisted hacker it tracks as Crafty Falcon is targeting organizations in the Banking, Financial Services, and Insurance sector in India. The agency says the campaign is active and ongoing, and that the tools behind it are built to run attack chains at machine speed.
The warning matters now because CERT-In says the activity is already reaching financial and crypto-related targets, including cryptocurrency exchanges and digital asset service providers. The attackers have used publicly available AI-driven offensive security tools such as ARTEX, PentAGI, Cairn, and CyberStrikeAI to generate and refine tailored attack scripts, adapt payloads to target responses, and rotate supporting IP addresses within hours to days.
That combination turns a familiar intrusion pattern into something harder to stop. CERT-In says threat actors have been exploiting internet-facing applications, exposed APIs, and privileged endpoints to steal payment aggregator and partner-bank API credentials, then invoking fund-transfer APIs directly from within the entities' own allow-listed infrastructure. The agency says that approach can bypass checks tied to loan creation, KYC, sanction screening, beneficiary verification, balance sufficiency, and per-transaction limits.
It also leaves a narrower trail for defenders to follow. CERT-In says the operators move stolen funds to attacker-controlled mule accounts across multiple banks, delete logs, tamper with endpoint security tools, and target cloud infrastructure to execute commands and deploy malicious payloads. It also warns that publicly accessible non-production environments can become a pivot point if shared credentials, tokens, or network paths are exposed.
The hardest part of the picture is what CERT-In does not say. It identifies Crafty Falcon as the track name for the activity, but not the people or group behind it, and it does not say how many Indian organizations have been hit. That leaves the threat active, the victims broad, and the attribution gap unresolved even as the campaign continues.
CERT-In paired the warning with its Artificial Intelligence Security Auditing Guidelines, which call for governance, security, privacy, fairness, transparency, resilience, and auditability in AI systems. The framework requires testing an AI agent's documented identities, authorized objectives, approved tool use, permission boundaries, and adherence to the principle of least privilege, along with human approval for consequential actions and emergency interruption for high-risk systems.
The guidance now sits alongside a wider series of attacks on financial and crypto-related entities, including an alert in October 2026 warning of multiple cyber attack campaigns targeting non-banking financial companies, digital lending platforms, fintech entities, payment service providers, and cryptocurrency wallet operators. For BFSI organizations, the message is blunt: the threat is not theoretical, and the controls around AI, APIs, and privileged access have become part of the same fight.